SimplAdmin
When an AI-Assisted Action Is Approved, What Must Change Before It Runs Again?
SimplSolutions Editorial Team · 7 min read
Published
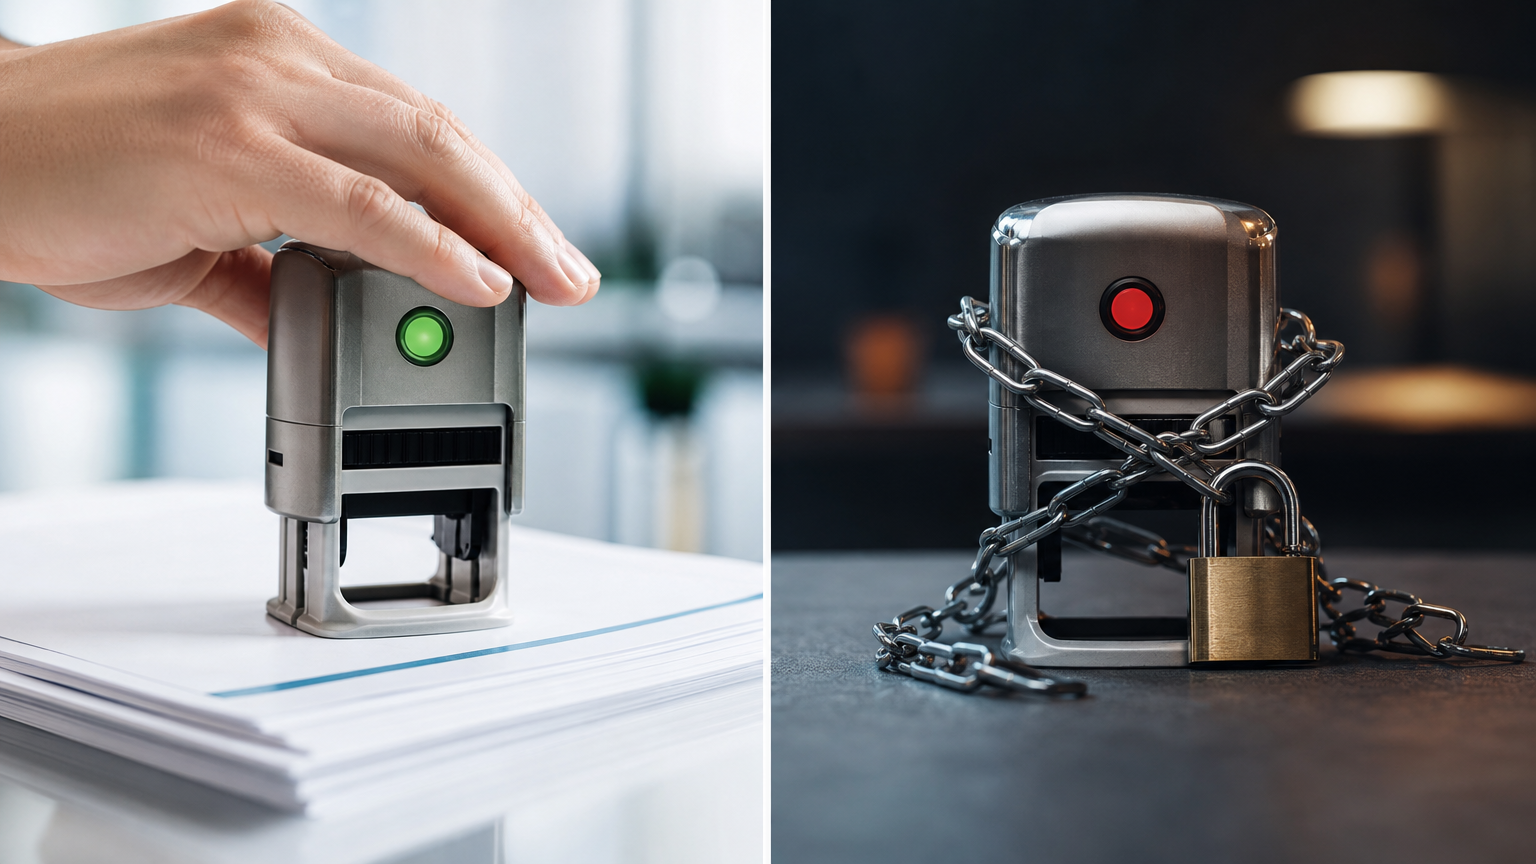
The operational problem is approval drift
An operations manager may approve an AI-prepared customer-reminder email on Monday. The message goes to the expected group, uses the expected wording, and serves a current business purpose.
The risk begins on the next run. A customer may have left the list. The offer or deadline may have changed. A calendar permission may have been expanded. The message may have missed its intended window and now be inappropriate. If a workflow treats Monday’s approval as indefinite permission, the human decision has quietly become broader than the person made it.
That is approval drift: the approved action stays in the workflow while the facts around it change.
The NIST AI Risk Management Framework is useful context. NIST describes the framework as voluntary and intended to help organizations manage AI-related risks and incorporate trustworthiness considerations into the design, development, use, and evaluation of AI products, services, and systems. For administrative operations, that context supports a practical control principle: an approval should be specific enough to inspect and limited enough to expire when its assumptions no longer hold.
Define what was actually approved
Before deciding whether a recurring action may run, separate two different decisions:
- Instance approval: “Send this prepared email to these recipients at this time.”
- Recurring-rule approval: “For this defined period and scope, prepare and send this class of reminder when the stated conditions are met.”
These decisions are not interchangeable. A person who approves one email has not necessarily approved every future email that resembles it. A person who approves a recurring rule has still not approved changes outside that rule’s boundaries.
An approval record can identify, in plain language:
- the business purpose;
- the authorized action, such as sending an email or creating a calendar change;
- the recipient, attendee, or record scope;
- allowed content and material variables;
- relevant mailbox, calendar, or system permissions;
- the execution window and any deadline;
- the accountable person or role;
- the expiration or review date; and
- conditions that require a pause and fresh review.
This is an editorial control framework, not a claim that NIST prescribes these fields. The practical objective is traceability: a reviewer should be able to understand what the human saw, what the human accepted, and what the workflow later attempted to do.
Worked example: a weekly customer-reminder email
Suppose an office manager approves a weekly reminder for customers who have not completed a required appointment form. The approved scope is narrow:
- the message explains the outstanding form;
- it goes to customers already identified by the office’s process;
- it runs on Wednesday morning;
- it uses a reviewed tone and approved contact details; and
- it remains valid through the current campaign period.
The first run is an instance. If the office manager wants the same class of reminder to run each week, the approval should say so explicitly and define the limits of that recurring rule.
On the next Wednesday, the useful question is not only, “Was something similar approved before?” It is, “Does this proposed run still fit the approved purpose, audience, content boundaries, permissions, and timing?”
If the answer is clear and yes, the action may proceed under the recurring authorization, subject to the organization’s own controls. If the answer is no or cannot be established, the action should pause rather than silently widen the approval.
Changes that should trigger fresh review
Recipients or affected records changed
A changed recipient list is not merely cosmetic. It can alter privacy exposure, customer expectations, and the business meaning of the action.
Fresh review may be appropriate when a new customer segment is added, an external address appears, a recipient is removed for a sensitive reason, or the underlying eligibility rule changes materially. Even if the email text is identical, the audience may no longer be the audience the manager approved.
For calendar work, the same consideration applies to new attendees, changed invitees, or a meeting that moves from an internal calendar to an external one.
Content or intended meaning changed
Small variable substitutions may fit within a recurring rule. A material change does not. Examples may include a new deadline, a different offer, a new policy statement, a changed attachment, a revised escalation instruction, or wording that creates a new commitment.
The relevant question is not whether text looks similar. It is whether a reasonable reviewer would regard the proposed communication as the same approved action. If the meaning, obligation, tone, or consequence changes, route it back for review.
Required permissions changed
An action may require access to a mailbox, calendar, customer record, or scheduling capability. If the permission context changes, the prior approval may not cover the new authority.
For example, a recurring reminder previously prepared through a shared mailbox may be proposed through an executive mailbox. A calendar action that once changed only an internal event may now include external attendees. Those are changes in operational reach, even if the visible task name is unchanged.
Business context expired or materially changed
Approvals depend on purpose. A reminder approved during an active campaign may no longer be appropriate after the campaign ends, a customer’s status changes, a deadline passes, or a policy is withdrawn.
A recurring rule therefore benefits from a validity period or meaningful review condition. “Run every Wednesday” is a schedule, not a business justification. The continuing question is whether the reason for the action remains true.
The execution window was missed
Timing can be part of an approval. If a reminder approved for Wednesday morning is held until Friday, sending it may create confusion or duplicate another process. A calendar change executed after a meeting has started may be worse than no change at all.
A missed window is a decision point. The prepared action can be preserved while an accountable reviewer decides whether it should be sent now, rescheduled, revised, or canceled. A late execution should not be treated as automatically authorized.
What to record and when to pause
A defensible record does not need to preserve every internal technical detail. It does need to preserve decision context that matters to the operator. Consider recording:
- the approved action and business purpose;
- whether approval covered one instance or a recurring rule;
- the approved scope and material boundaries;
- the proposed run’s recipients, content version, permissions, and scheduled time;
- the identity or role of the approving human;
- the approval time and validity period;
- differences detected before execution; and
- the final outcome, including whether the action ran, was edited, paused, or rejected.
A pause should be a normal control state rather than an exceptional failure. Route an action to a human when the recipient scope is outside the approved boundary; content introduces a new commitment, deadline, policy, or sensitive topic; the action relies on a different permission set; the original purpose is uncertain; the execution window has passed; or the proposed action cannot be compared reliably with the approved scope.
Presenting the proposed action, prior approval, and detected difference together makes the decision concrete. The reviewer can approve the instance, update the recurring rule, reject the action, or end the rule.
A practical decision test for operations managers
Before allowing a recurring AI-assisted administrative action to run, ask five questions:
- Same purpose? Is the business reason still current?
- Same scope? Are recipients, records, attendees, and affected systems within the approved boundary?
- Same meaning? Does the content remain materially consistent with what was reviewed?
- Same authority? Will the action use the same relevant permissions and operational reach?
- Same timing? Is it still within the approved execution window?
If all five answers are clear, a recurring authorization may be suitable for the next run, subject to the organization’s policy and risk tolerance. If any answer is no—or cannot be established—the action should pause for review.
The operating principle: approval is bounded permission
The goal is not to require a person to reapprove every harmless repetition. It is to prevent repetition from being mistaken for authorization after the underlying facts change.
For administrative workflows, a sound approval is bounded by purpose, scope, content, authority, and time. A recurring rule can reduce unnecessary review when those boundaries remain stable. It should not erase them.
NIST’s framework provides voluntary risk-management context, while each organization decides its own controls, accountability model, and review thresholds. The important operational choice is to make those boundaries explicit rather than leaving them to an implicit assumption in an automated workflow.